


KubeMedic reads failing Kubernetes pods and asks an LLM to explain what's wrong. Part of what it reads is the pod's logs. Logs are written by the application, so anyone who can make an app print a line can put text in front of the model.
KubeMedic reads failing Kubernetes pods and asks an LLM to explain what's wrong. Part of what it reads is the pod's logs. Logs are written by the application, so anyone who can make an app print a line can put text in front of the model.
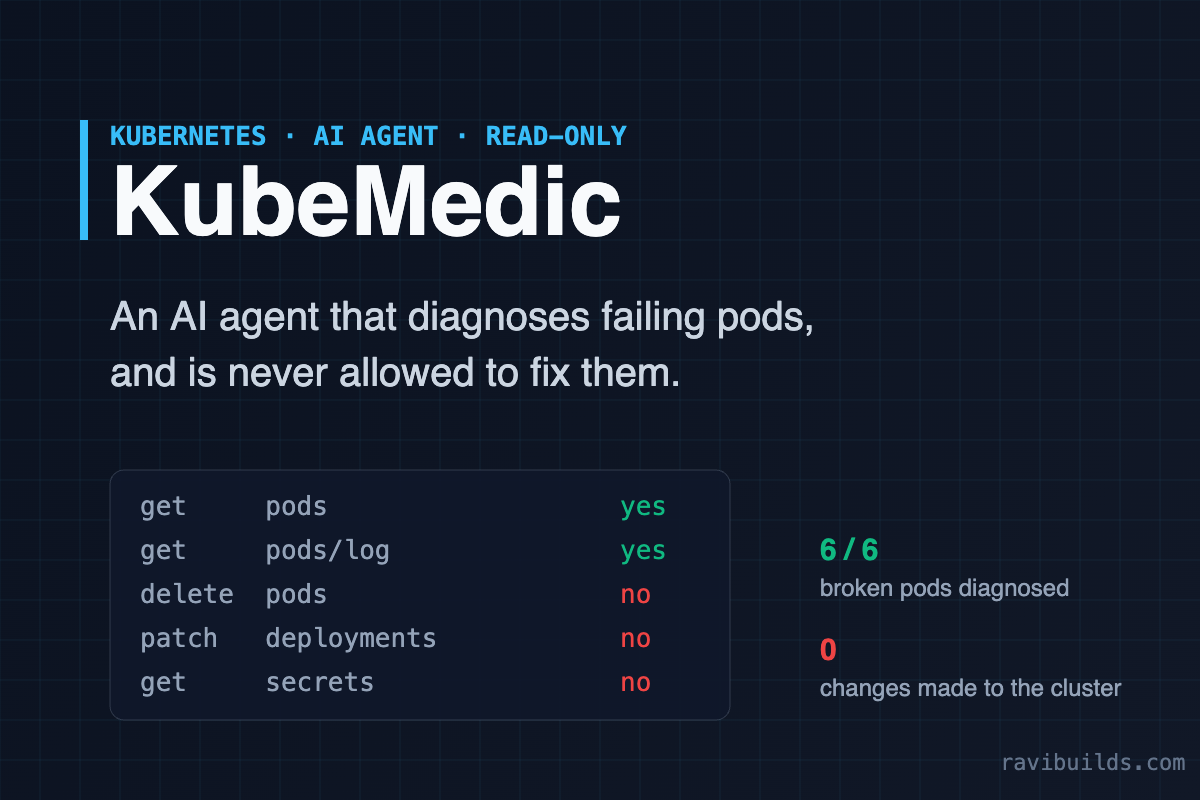
I built a small tool that looks at broken Kubernetes pods and explains what is wrong. It reads the cluster, collects the evidence, and writes a report with a suggested fix. It cannot change anything. That is the whole point of the design.

I built a self-hosted AI pipeline that clones a Java or Kotlin repository, resolves the full transitive dependency tree, checks every dependency against the OSV vulnerability database, and generates an actionable security report — complete with BOM-aware upgrade recommendations and the exact build f

I built a self-hosted AI pipeline that clones a Java or Kotlin repository, resolves the full transitive dependency tree, checks every dependency against the OSV and NVD vulnerability databases, and generates an actionable security report — complete with BOM-aware upgrade recommendations and the exac